 Docs
Compliance evidence
Every identity and control event is committed to a tamper-evident, independently-witnessed ledger you check yourself, keyless. Evidence you can recompute, not a checkbox we assert.
Most tools ask an auditor to trust a dashboard. Whisper Endpoint commits each identity and each control event (mint, policy change, revoke, contain) to an append-only transparency log. The identity, the containment and the timestamp are cryptographically anchored, not asserted in a PDF, and anyone can verify them with stock tooling and no Whisper account. Our own API is never in the trust decision. This is the one thread that runs through every layer of the product: verify it yourself.
Verify without taking our word for it
- Identity is DNSSEC-validated to the IANA root and pinned in DANE; check it with
diganddelv. The full walkthrough is at Verify an identity. - Events are committed to the log; each carries an RFC 6962 inclusion proof that recomputes to a signed root, and a
/consistencyproof shows the log only ever appended. - Timestamps are anchored with OpenTimestamps into the Bitcoin chain, so an event cannot be back-dated.
- Independence comes from a witness: a second party cosigns the log's checkpoint, so a split view served only to you does not verify.
Read the checkpoint
The log publishes a signed checkpoint anyone can fetch, keyless. This is a real capture, dated 2026-08-30:
$ curl -s https://rdap.whisper.online/checkpoint
whisper.online/ledger/g2
208004
Yov6qfhUW0N3MRt2TTy3DXx5Bg5YmpnwIi4/aS16GaQ=

— whisper.online/ledger/g2 1A5XOkHIFQVmYUUK1+kstq4e1bq+rOeu2YiymyrNAx0EDA1kmnp1ZlnB2V5+/29BxFGopDmoM4ObZrxuDtiowHn1agw=
— markovianprotocol.com/witness QbiCfwAAAABqk68xj+uePM5lYRSEmElxcXdzpIWrg3zCf8ZzKpA3W6HWv0P5vWsp5DVcI0ZeDO2KSQW5c62AaDm9Dt8lO9q8Wpm3Bw==
The two signature lines above are shown byte-exact: the C2SP signed-note format's own delimiter is an em dash, not a hyphen, and this page quotes the live wire format rather than substituting a house-style character into someone else's protocol.
Read top to bottom, it is a signed note in the C2SP format:
whisper.online/ledger/g2is the log's origin, its identity.208004is the tree size, the number of entries committed at this checkpoint.- The base64 line is the Merkle root hash over every one of those entries.
- The two signature lines follow: the log's own Ed25519 signature (fleet key
8a3a5df0), then the independent cosignature frommarkovianprotocol.com/witness. On the wire each is prefixed with the signed-note delimiter and its signer's name.
Stated at its earned level. The witness set is pinned at n=4, k=2 (Mullvad, TrustFabric, Geomys, Markovian). Today one independent witness cosigns, so the claim is tamper-evident and independently witnessed, not yet publicly verifiable in the split-view-resistant sense. The served claim self-heals to publicly verifiable once the second independent witness enrolls; we will not print the stronger word before the quorum is real.
To go from the checkpoint to a specific event, fetch that event's inclusion proof and recompute the root yourself. It is a short hash chain (a few lines of python hashlib) that has to land on the exact base64 root above, or the proof fails. Nothing in that computation calls Whisper.
What lands in the ledger
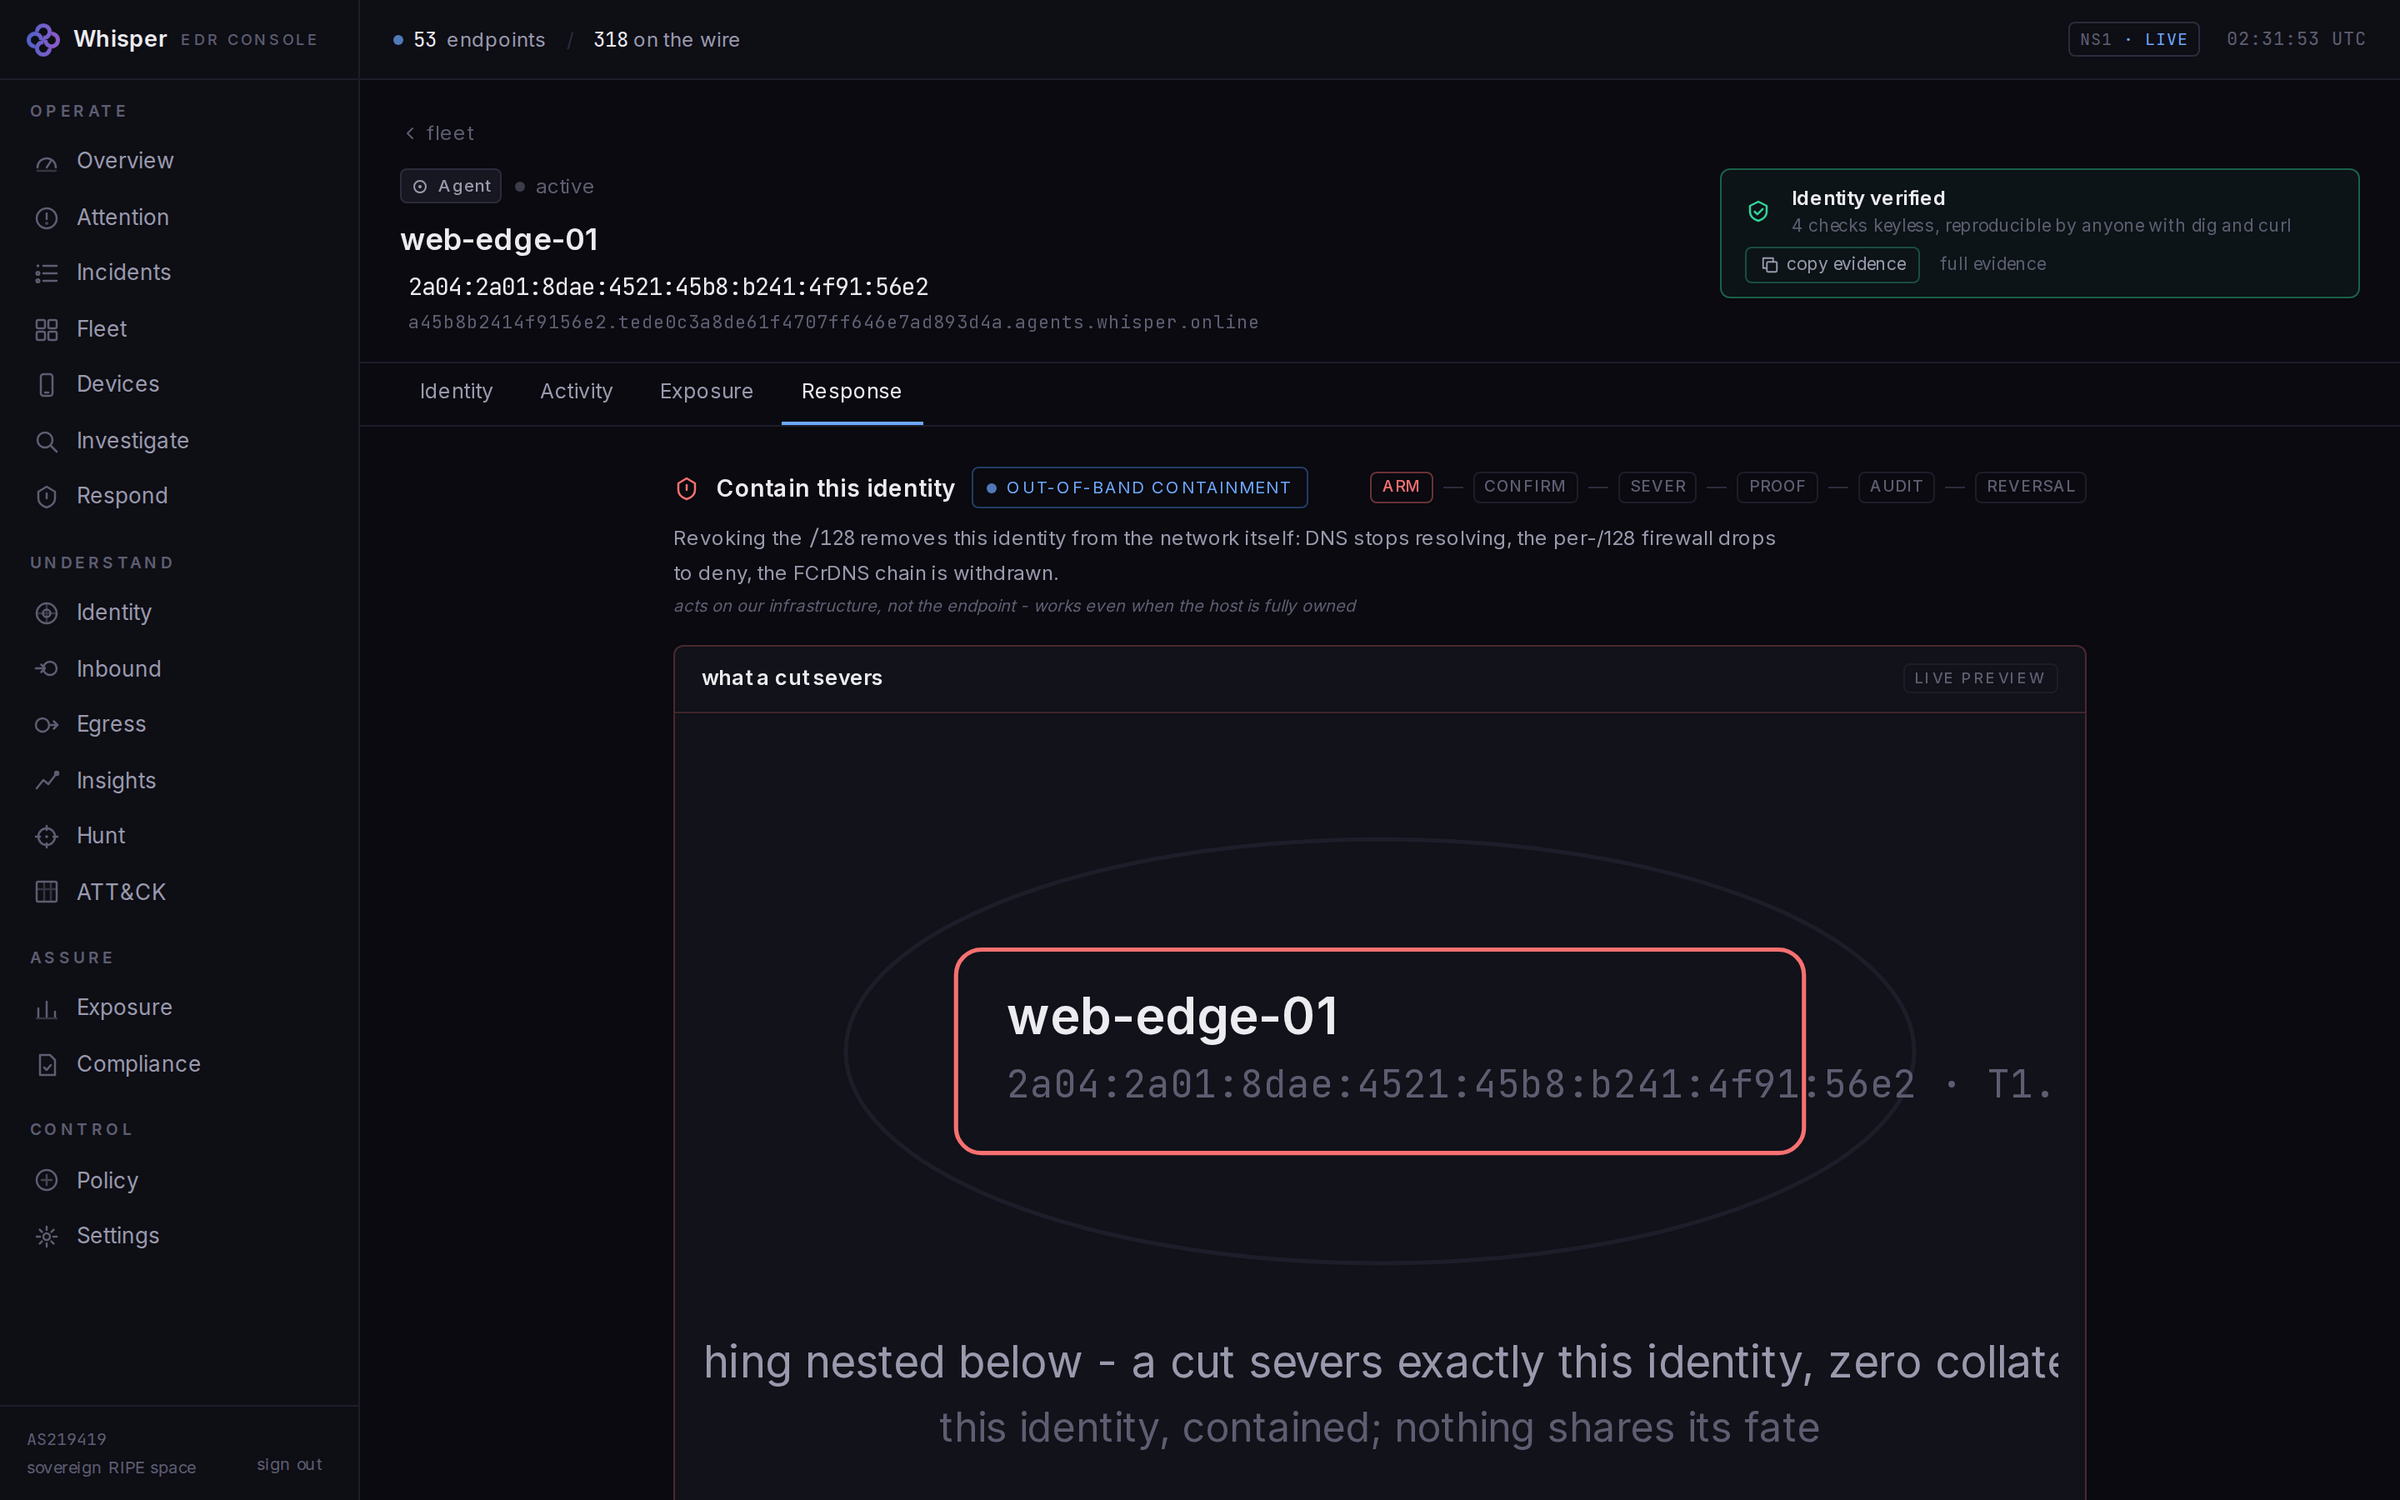
Identity lifecycle events are committed as they happen: a /128 mint, a policy change, a revoke. Containment is committed too, and a contained action carries a keyless third-party proof at /api/contain/action/<ledgerId> plus a durable audit entry, so a cut is provable after the fact and not just a line in a log the operator controls.
Governance writes get the same treatment as the cut itself. Every per-agent egress firewall write, every budget kill, every run scope lands in the durable containment audit trail on the same footing as a revoke, on every outcome, so "who narrowed this agent's egress, when, and to what" is answerable from evidence, not from memory. The policy surface these entries come from is documented in Fleet, logs and console.
Erasure and audit coexist. When an identity is released, everything that identified it is gone from the public record: the RDAP object for that address carries no handle, no ldhName, no registrant entity and no registration event, only the covering allocation and a remark saying there is no assignment. Meanwhile the log's consistency proof still verifies, because the ledger commits to hashes, not to personal data. That is how GDPR Article 17 erasure and an immutable append-only audit live on the same system.
Jurisdiction you can read off the address disabled by default · enabled per deployment
For programs with a data-residency clause, the identity plane can carry jurisdiction as evidence. Enabled, each /128 is allocated inside a country-tagged sub-block of your prefix, and the tag is published as jurisdiction in the identity's public RDAP record and the standard geofeed, so a regulator or auditor can read an agent's jurisdiction off its address with a keyless lookup, not off an attestation. It is disabled by default, allocation stays byte-identical until it is enabled for your deployment (ask us), and a jurisdiction lookup can never block an allocation. Separately, resolution-plane geography policy (country allow and deny lists, deny wins) is live and per lookup; that is a control, and its writes land in the same ledgered trail as every other policy change. Both halves are documented in Fleet, logs and console.
The per-control mapping
Whisper Endpoint is a control-and-evidence layer inside your program. It provides a control, or gives audit evidence toward a requirement, per framework:
| Framework | What it provides |
|---|---|
| SOC 2 | The logical-access and deprovision controls (CC6.1 / CC6.2): identity plus the one-call revoke, with a ledgered, recomputable trail. |
| ISO 27001 | The identity-lifecycle control (A.5.16): mint, govern, revoke, each committed to the log. |
| HIPAA | Audit evidence toward unique-ID and entity authentication (§164.312). |
| PCI DSS | A network and component-identity control (Req 1 & 8): the per-agent egress firewall and the identity, both ledgered. |
| CMMC | Evidence toward the access-control and audit / accountability practice areas. |
| NIS2 | Audit evidence toward access control and secured communications (Art. 21). |
| DORA | Audit evidence toward cryptography and in-transit protection (Art. 9). |
The framing
Whisper Endpoint provides a control, gives audit evidence toward a requirement, or complements your sector's own PKI. It never makes you or your organization compliant or certified, and it never guarantees compliance. Your auditor does that; this is the evidence you hand them, and they can recompute all of it without taking our word for it. EU-run infrastructure on our own address space keeps that evidence resident where you can point to its jurisdiction.